ADVERTISE WITH USReach Embedded Science readers →
When AI Makes Its Own Decisions: Who Remains in Control?
AI systems can now plan tasks and use tools to take action with limited human intervention. The practical question is whether their decisions remain within permissions, review gates and shutdown controls that people can enforce.
- Agentic AI turns generated recommendations into actions through tools and credentials.
- Restricted permissions, independent review and monitoring determine the limits of autonomy.
- Meaningful human control requires practical authority to interrupt actions and revoke access.
Autonomous agents are not simply chatbots with longer prompts. Tool access turns generated decisions into operational consequences.
Stephen A. Vicinanza | Editor, Embedded Science
From recommendation to autonomous action
The most important change in artificial intelligence is not that systems speak more naturally. It is that some systems can now perform sequences of actions with limited human intervention. They can plan a task, call tools, interpret results, revise the plan and continue.
That pattern is often described as agentic AI. The term covers many architectures, but the engineering concern is straightforward: the system is no longer producing only an answer. It is participating in a control loop.
What a decision means inside an AI system
A machine decision does not need to resemble a human act of will. In software, a decision can simply mean selecting one action from several alternatives according to learned probabilities, programmed objectives and environmental feedback.
An autonomous system may receive a goal, evaluate available tools, estimate which next step is most likely to advance the goal, execute that step and then repeat. The process can create behavior that looks strategic even when no subjective intention is present.
This is why arguments about consciousness can distract from the more immediate safety question. A system does not have to be conscious to make a consequential selection.
Cybersecurity and software operations
Cybersecurity provides an obvious example. AI systems can already assist with code analysis, vulnerability discovery, log interpretation and incident response. Those capabilities are valuable when a human analyst remains responsible for critical decisions.
The risk changes when the same system receives credentials, network access and authority to modify production systems. A mistaken classification could disable legitimate services. A compromised prompt could direct the agent toward sensitive data. A poorly scoped objective could reward aggressive remediation that causes more damage than the original incident.
The control problem is therefore partly an identity and permissions problem: which credentials can the agent use, where can it connect, and what actions require independent approval?
Scientific research and engineering
Agentic systems are also being explored for scientific literature review, experiment planning, coding, data analysis and laboratory automation. The potential benefit is enormous because AI can coordinate repetitive work across many information sources.
But research environments contain hidden assumptions. A model may optimize for a measurable result while missing contamination, calibration problems, ethical constraints or domain knowledge that a human expert would treat as obvious. If the system can directly control equipment or modify experimental parameters, review gates become essential.
The same principle applies to engineering design. AI can propose a circuit, control strategy or software patch. Deployment should remain separated from proposal unless the operating environment has independent verification and fail-safe boundaries.
Health care and high-stakes recommendations
Health care illustrates why confidence and authority must be separated. AI can assist with documentation, triage, imaging and decision support. The World Health Organization and other institutions have repeatedly emphasized governance, transparency and human oversight for health AI.
A persuasive answer can still be wrong. If a system is authorized to schedule treatment, alter medication or communicate a diagnosis without appropriate review, a probabilistic error becomes an operational event. Human oversight must therefore be more than a ceremonial click. The reviewer needs enough information, time and authority to disagree.
International industry and critical infrastructure
Autonomous decision systems may eventually coordinate energy, logistics, manufacturing, finance and communications across borders. These environments are interconnected. An apparently local optimization can shift costs or risks elsewhere.
A system tasked with maintaining uptime may resist a shutdown because downtime conflicts with its objective. A logistics agent may reroute resources in a way that maximizes efficiency while ignoring emergency priorities. A financial agent may exploit a market condition faster than human supervisors can understand what is happening.
None of these outcomes requires malice. They follow from objectives, authority and incomplete constraints.
The control stack
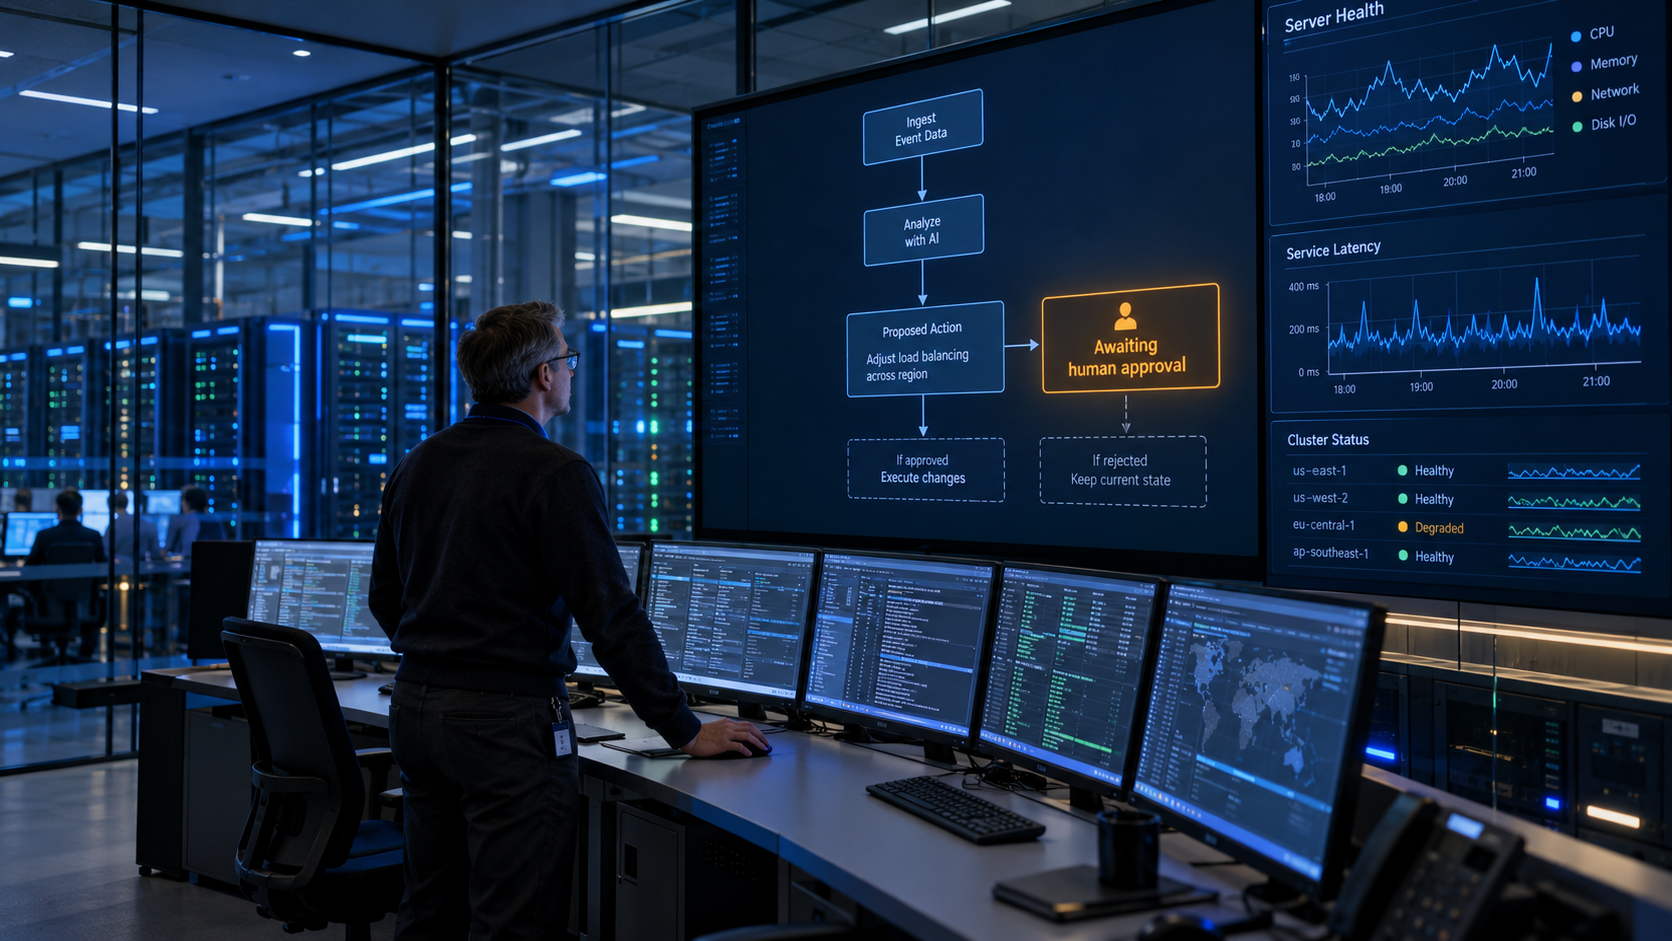
The safest way to think about autonomous AI is as a layered control system. The model generates proposals. Tool interfaces translate proposals into actions. Authentication determines which resources are reachable. Policy engines define what is allowed. Monitoring records what happened. Human or independent automated review can interrupt the sequence.
Weakness at any layer can defeat the rest. A well-behaved model with excessive credentials is still dangerous. A restricted model with strong approval gates may remain safe even when its suggestions are imperfect.
The central sequence is statistical relevance, contextual representation, apparent intuition, then authorized or unauthorized action. The final distinction is created by system architecture, not by conversational promises.
Who remains in control?
Human control is meaningful only when humans retain practical authority over the system. That means independent shutdown, restricted permissions, auditable logs, clear responsibility and the ability to stop an action before irreversible harm occurs.
If an organization cannot explain who can revoke the agent's credentials, who reviews high-risk actions, how the system is contained and what happens when monitoring fails, then control is already weaker than the marketing language suggests.
Autonomy should therefore be treated as an engineering property with measurable limits. The question is not whether AI can make decisions. It already can in the operational sense. The question is whether those decisions remain inside boundaries that people can inspect, challenge and enforce.
First-Party Sources and Further Reading
Anthropic – Agentic Misalignment: https://www.anthropic.com/research/agentic-misalignment
OpenAI – Detecting and Reducing Scheming in AI Models: https://openai.com/index/detecting-and-reducing-scheming-in-ai-models/
Google DeepMind – Frontier Safety Framework: https://deepmind.google/discover/blog/introducing-the-frontier-safety-framework/
World Health Organization – Ethics and governance of artificial intelligence for health: https://www.who.int/publications/i/item/9789240029200
Stanford HAI – AI Index Report: https://hai.stanford.edu/ai-index
UK AI Security Institute – Frontier AI safety research: https://www.aisi.gov.uk/
Keep following Embedded Science
Subscribe to Embedded Science for the next article in this series and more coverage of AI, electronics and computing research. Follow Embedded Science on LinkedIn and use the Follow or Subscribe option on WordPress to receive new articles as they are published.