ADVERTISE WITH USReach Embedded Science readers →
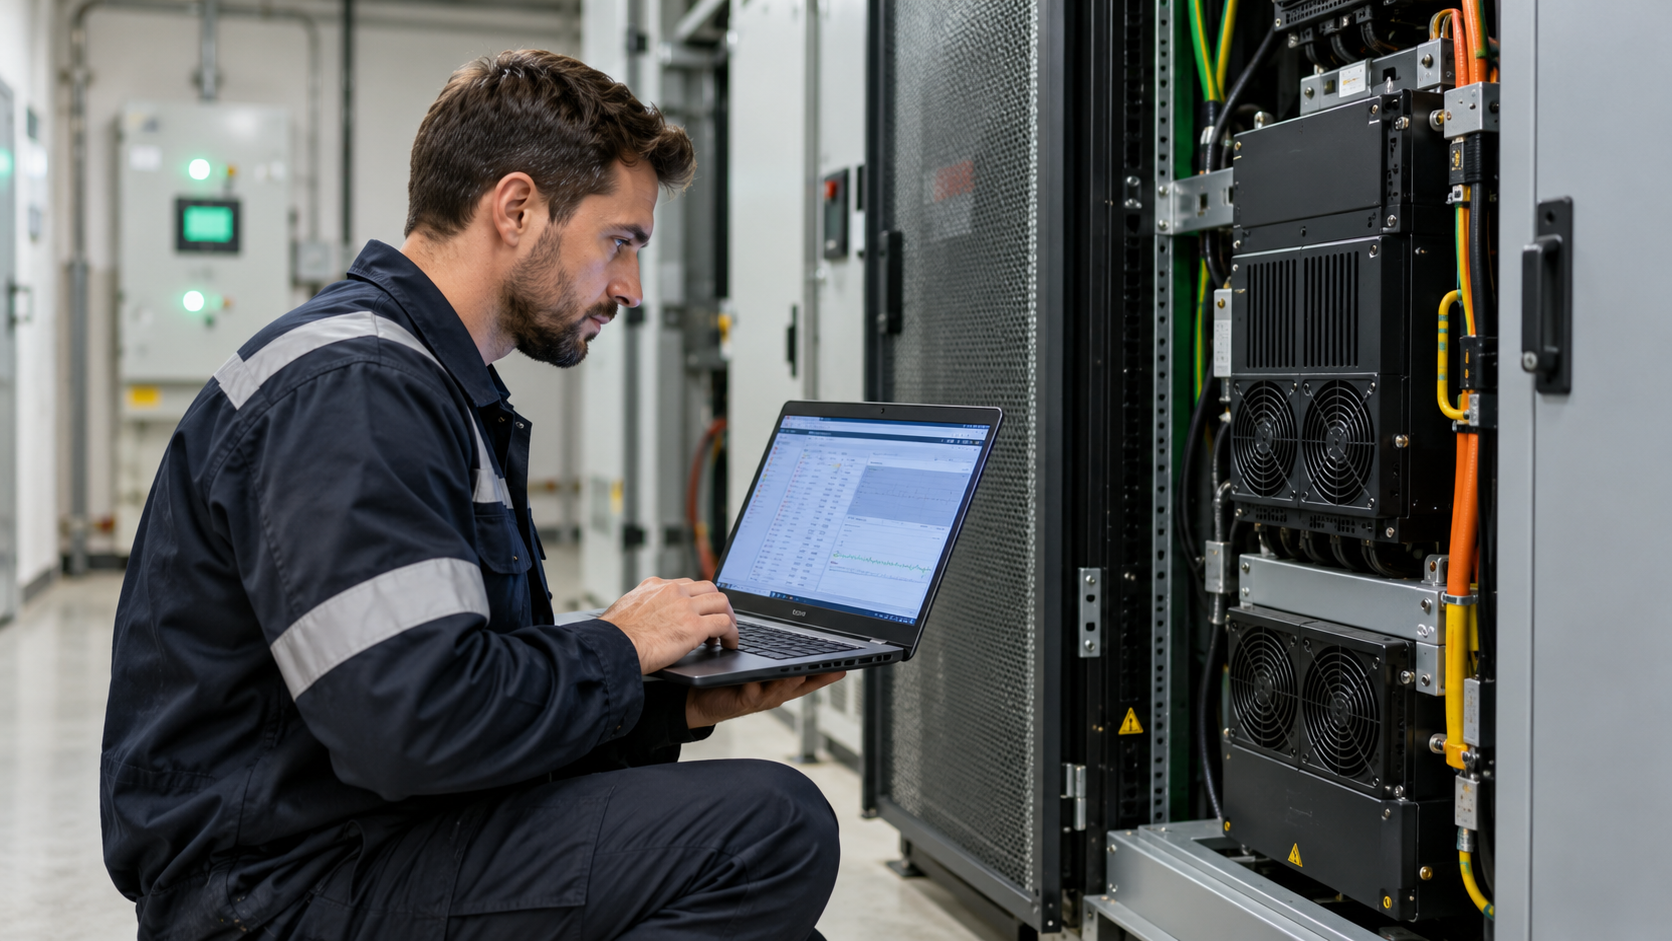
Infineon’s XDP8HD40S-1 Adds Digital Protection to AI Server Power
Stephen A. Vicinanza | Embedded Science
An AI server power architecture needs a defined response when equipment is connected, disconnected or develops a fault. Infineon’s new XDP8HD40S-1 brings digital control and event information to that protection problem.
- Infineon introduced the controller on October 12 for high-voltage DC architectures.
- Digital protection settings need to be tied to the external power stage.
- Event records can support investigation without proving root cause alone.
Protection becomes a configurable function
Infineon describes the XDP8HD40S-1 for systems using ±400-V and 800-V DC distribution. The company identifies digital safe-operating-area control, programmable protection, a PMBus interface and a black-box recording function. It also describes an integrated driver for external power-stage implementations. These are attributed product capabilities; they do not establish the behavior of a complete server installation.
The configurable nature of the protection is particularly relevant to a design review. A setting should correspond to a documented system requirement, rather than being accepted because it allowed a prototype to start successfully. Teams need to know who owns those settings, how changes are reviewed and how the installed configuration can be identified later.
The external circuit still matters
A protection controller operates within a physical assembly. Engineers should evaluate the chosen switching devices, the load, the source and the connection arrangement together. That evaluation determines whether the intended protective action is possible under the conditions the system may encounter.
For example, an illustrative design could pass its ordinary operating test and still require additional work to establish how it handles an abnormal connection sequence. The appropriate conclusion would be that normal operation has been demonstrated, not that all fault conditions have been addressed.
This is also where a configurable device can create useful flexibility and additional responsibility. Adjustability is valuable when it lets the team fit protection to a defined load. It is less useful when the technical record does not explain why a particular setting was chosen.
Make event records answer a question
The black-box feature is a strong editorial lead because it connects protection to diagnosis. A fault record becomes useful when an engineer can interpret what was measured, when it was captured and what the controller was doing at that moment.
An evaluation should therefore begin with known events. The team can compare the retained record with an independent reference and determine whether it distinguishes the conditions that matter to maintenance. It should also examine what happens when several events occur close together and how records are retrieved after an interruption. Those are questions for testing, not performance findings reported here.
Operational access needs planning as well. A maintenance technician may need to inspect a record without being allowed to change protection thresholds. Keeping those responsibilities clear helps preserve the value of both the evidence and the configuration.
Judge the architecture, not the label
Terms such as digital protection and high-voltage readiness are starting points for inquiry. The engineering evidence should show the operating envelope, the tested disturbances and the response of the actual assembly.
Infineon’s announcement broadens the discussion of AI power beyond conversion efficiency. It points toward infrastructure that can both react to an electrical problem and leave evidence about it, provided the implementation and its settings receive the same scrutiny as the controller specification.
Configuration is an engineering artifact
When protective behavior can be adjusted, the configuration deserves version control and review appropriate to its role. A team should be able to recover the settings used in an evaluation and compare them with the settings installed in the field. Otherwise a successful test can become disconnected from the equipment it is supposed to represent.
An illustrative change review would state the requirement behind a new setting, the expected effect and the test needed to accept it. It would also record any conditions that remain outside the evaluation. This creates an accountable path from an engineering decision to a deployed configuration without assuming that every adjustable parameter should be changed.
Establish the evidence before an incident
Diagnostic functions are most useful when their interpretation is understood before a failure occurs. Teams can deliberately generate known events in a controlled evaluation and learn what the records actually show. They can then write a maintenance guide that distinguishes observations from conclusions and identifies when further investigation is needed.
The retrieval process should be tested as part of that exercise. A record that exists but cannot be accessed by the authorized service team may have limited operational value. Conversely, a convenient diagnostic interface should not silently become an unrestricted route to changing protection settings. The design should make those separate responsibilities explicit.
Ask what the comparison really includes
A product evaluation should define the external circuit, load and operating conditions before comparing results with another approach. It should also state whether the assessment concerns protection response, diagnostic visibility, installation effort or some combination of them. Those are distinct benefits that may require different tests.
This gives reporting a more useful vocabulary. A team can say it demonstrated a response to a defined event, or that a record helped distinguish two explanations, without claiming that the controller eliminates all downtime. Infineon’s protection and monitoring features are worth examining precisely because they can be connected to concrete engineering questions. A documented, bounded result will tell customers more than an unqualified claim that their next AI installation is protected.
Follow the configured device into service
The final acceptance record should identify the controller settings and the assembly in which they were evaluated. Service information can then be connected to that record when an incident occurs. This closes a practical gap between prototype testing and field investigation. The organization gains a clearer account of what it installed, why it chose that behavior and which evidence should be reconsidered when operating conditions or hardware change.
That continuity is part of making protection useful beyond the initial demonstration.
Subscribe free to Pulse, then choose Pulse AI in your subscription preferences for research and engineering updates. Explore UniStack EECS, and follow Embedded Science on LinkedIn and WordPress for future coverage.